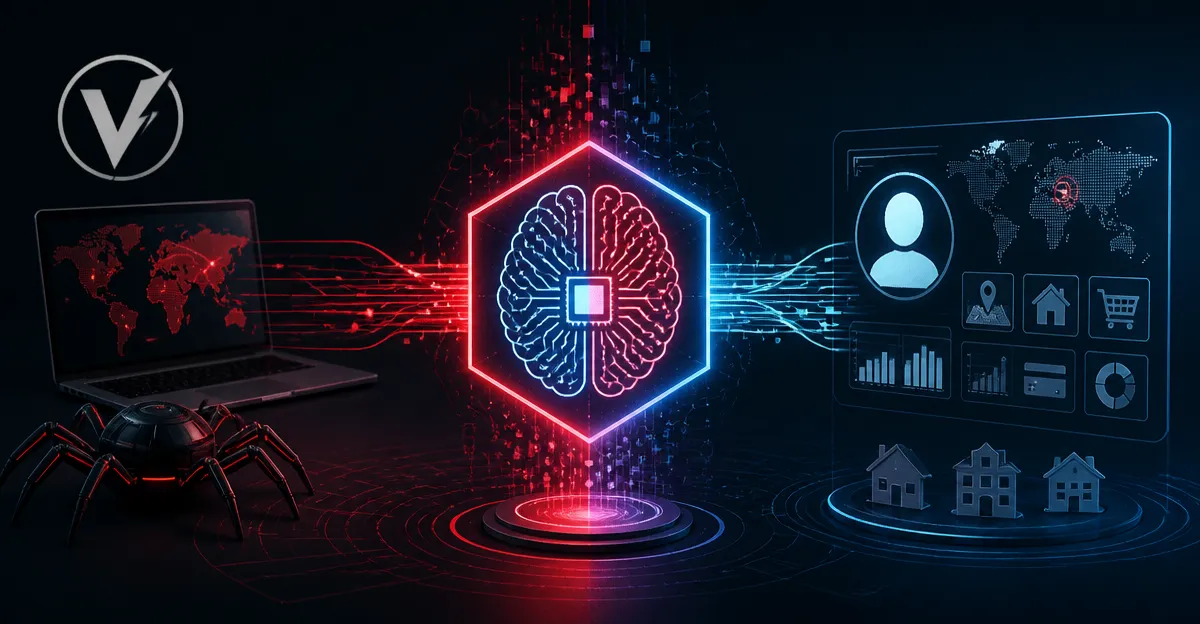
November 2, 2026, (Inside AI) — Security researchers at Cisco Talos have uncovered a new strain of infostealer malware that uses commercial large language models to automatically profile victims and rank them by value. The malware, dubbed Volta-Autodoxer, was found using Talos's new CAIRN framework, which is designed to identify hacking tools that incorporate AI capabilities. It is unclear whether Volta-Autodoxer has been used in active attacks.
The discovery highlights how mainstream LLMs from Anthropic, Google, and Moonshot AI are being repurposed to augment established malware. By automating tasks that once required manual effort, attackers can compress the timeline of an intrusion and focus on high-value targets faster.
Infostealers are a common type of malware hidden in counterfeit software. They vacuum up usernames, passwords, authentication tokens, cookies, credit card data, and more from compromised systems. Several major data breaches have been traced to credentials stolen by such malware. Volta, the underlying stealer, is described by researchers as mature and broad in scope. It now targets younger internet users with active digital lives, sweeping for browser-stored passwords, Microsoft OAuth tokens, cookies, payment cards, and crypto wallet seed phrases. It has also been redesigned to target sessions on Discord, Telegram, Steam, and Roblox.
After collecting data, Volta feeds its findings into AI models through OpenRouter, a gateway that can send prompts to multiple providers. It starts with Anthropic's Claude Opus 4.6. If blocked by guardrails, it falls back to Kimi K2, an open-weight model from China's Moonshot AI. If that fails, it uses Google's Gemini 2.5 Flash. The malware sends a 240-word prompt instructing the model to act as a forensic intelligence analyst. The prompt asks for an executive summary of the victim, what they do, what they are worth, and a summary of their operational security. It also tells the model to connect dots across fields, such as checking whether a Wi-Fi password matches a last name, and to go deep, not wide.
Read: AI lowers cybercrime barriers
"Volta is pretty mature as a stealer. It casts a pretty wide net for what it collects. It compiles all of those things together, ultimately producing a serialized dossier that it can send to a couple LLM models. It's asking the model to act like an intelligence analyst and produce structured citation-backed assessment of the victim. It's like a prioritisation and analysis function," Ryan Fetterman, a security researcher at Cisco Talos, was quoted as saying by Wired.
"We're seeing more advanced capabilities accessible to lower-level sophistication attackers. It's really interesting and disturbing [...] If you're able to identify your high-value targets faster, you probably have a better chance of using their credentials or authenticating using stolen tokens more often than maybe you would have if you had to do that triage yourself," he added.
The use of multiple LLMs with fallback logic shows a deliberate effort to bypass safety guardrails. This approach lowers the barrier for less-skilled attackers, who can now leverage AI to perform triage that once required human judgment. The researchers note that the malware was observed sending a structured prompt with bullet points and a numbered list, indicating a level of sophistication in how it interacts with the models.
This is not the first time hackers have used LLMs for coding or analyzing stolen data. Recently, researchers at Crowdstrike reported four distinct hacking groups using AI tools to compromise dozens of targets globally, including government entities and businesses in health care, retail, and travel.
The emergence of Volta-Autodoxer underscores a broader trend: AI is not just a defensive tool but also a force multiplier for attackers. As commercial models become more capable, the line between advanced and commodity threats blurs. Defenders must now account for adversaries who can automate the most tedious parts of an attack, from victim selection to data analysis.
Read: CrowdStrike AI hacking tools
Talos's CAIRN framework represents an early attempt to systematically detect AI-enhanced malware. However, the cat-and-mouse game is likely to intensify as attackers refine their prompts and evade detection. For now, Volta-Autodoxer serves as a warning that even conventional infostealers can become significantly more dangerous with a little AI assistance.